
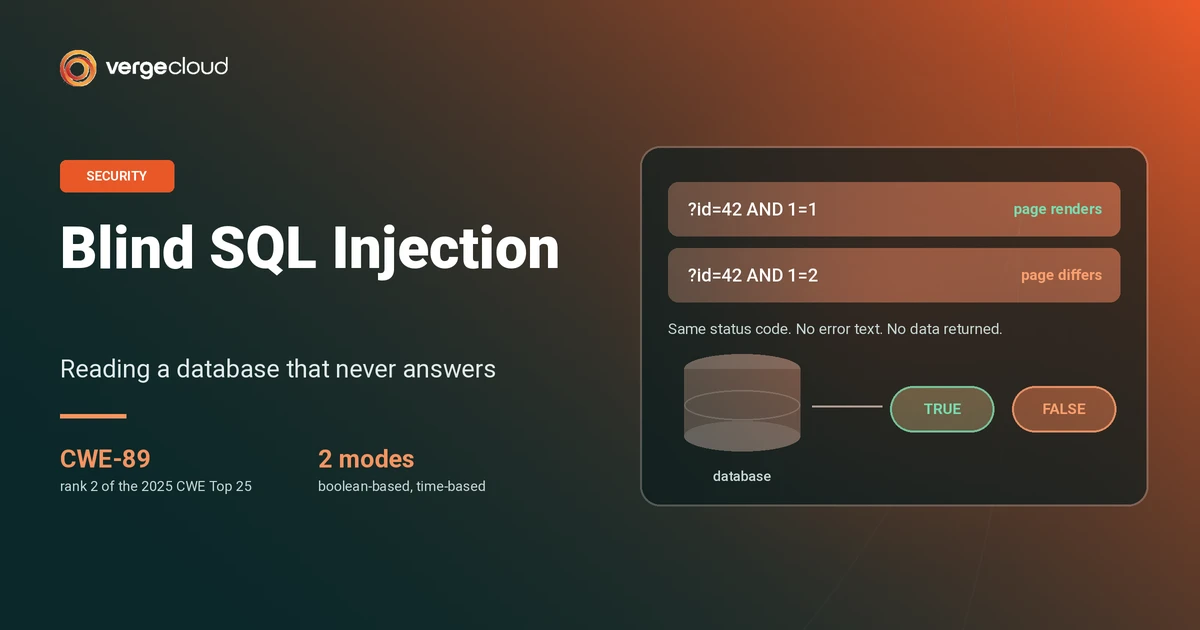
Blind SQL injection is a form of SQL injection where an attacker manipulates a database query but never sees the query result on the page. Instead of reading returned rows or an error message, the attacker asks the database a series of true or false questions and reads the answer from the application’s behavior: whether the page changes or how long the response takes. It is the same class of flaw as classic SQL injection (CWE-89), only harder to spot because the channel is behavioral, not visual. This guide breaks down how the attack works, the boolean-based and time-based techniques behind it, how attackers automate it, and the layered controls that detect and prevent it.
Key Takeaways
- Blind SQL injection extracts data through the application’s behavior, not its output. The vulnerable query runs, but its result is never displayed.
- There are two core techniques: boolean-based, which reads a true or false page difference, and time-based, which reads an injected delay.
- Each request reveals roughly one bit, so attackers automate the process with tools like sqlmap and send hundreds to thousands of near-identical requests.
- The high request volume against a single parameter is the defender’s best detection signal.
- SQL injection sits at rank 2 on the 2025 CWE Top 25, and blind variants appear in fresh CVEs every month.
- Parameterized queries are the only fix that removes the vulnerability. Edge controls like a WAF and rate limiting cut noise and buy time.
How Blind SQL Injection Differs From Classic SQL Injection
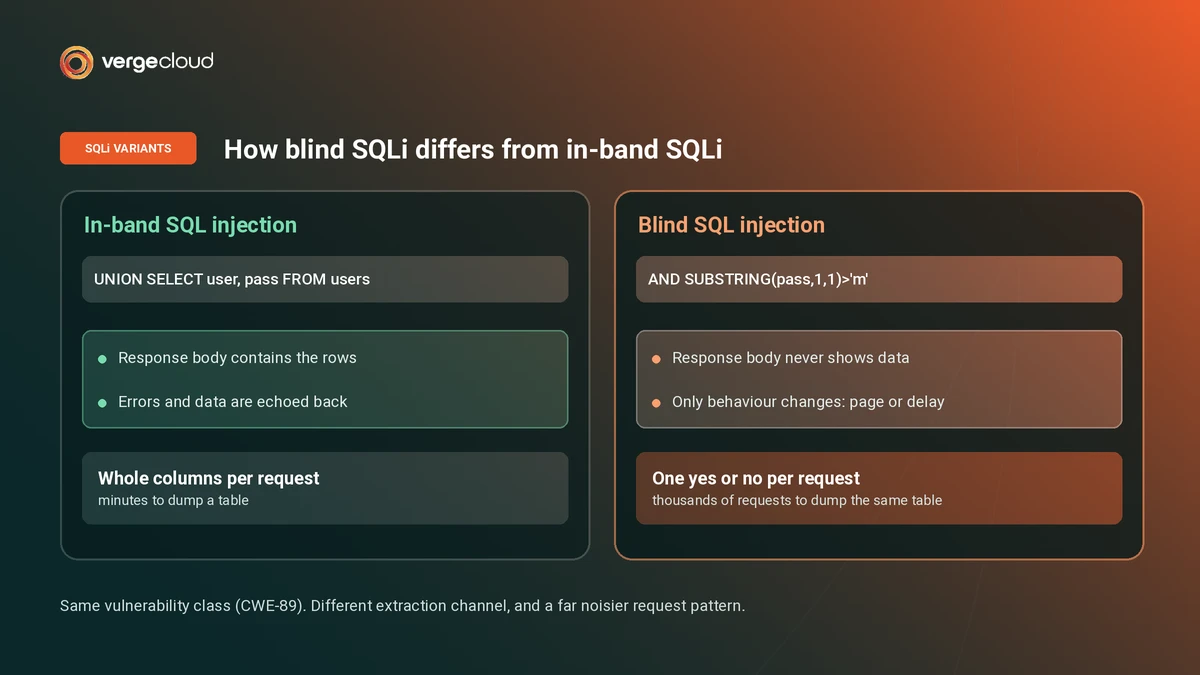
The difference is the retrieval channel. In classic in-band SQL injection, the attacker sees data directly: the query result is rendered on the page or leaked through a database error message. In a blind injection attack, the application suppresses errors and never echoes query output, so the attacker cannot read data the normal way.
The vulnerability is identical. Untrusted input reaches the SQL engine as code rather than data. What changes is how the attacker gets the answer out. When the page looks the same no matter what you inject, you fall back to inference: send a query that behaves one way if a condition is true and another way if it is false, then read that behavior.
This is why blind SQL injection is also called inferential SQL injection. Nothing is transferred out of the database directly. The attacker reconstructs the data one answer at a time by watching the application respond.
A page that returns a generic error or a plain HTTP 500 is not proof of safety. It often just means the application hid the database error, which is exactly the condition under which blind SQL injection thrives.
Because the page hides its results, teams often lean on their edge layer to catch the intrusion attempt before it reaches the database. A well-tuned advanced web application firewall inspects request bodies and query strings for the inference patterns these attacks rely on, which we return to in the prevention section.
How Boolean-Based Blind SQL Injection Reads One Character at a Time
Boolean-based blind injection sends a query that forces the application to return one response when a condition is true and a different response when it is false. The attacker reads that difference and infers a single fact about the data.
Start with a parameter that feeds a query, for example a product lookup by id. The attacker first confirms the flaw with two probes that should behave differently:
If the two responses differ, the parameter is injectable and the attacker now has a reliable oracle. From here the goal shifts to reading real data, one character at a time, using string functions:
Each probe halves the search space, so a binary search finds one character in about seven requests. Repeat for every position and the attacker recovers the whole value. The technique works even when the page content never changes visibly, as long as some observable behavior differs between true and false.
Why boolean probing is slow but reliable
Reading a single 8-character password can take roughly 56 requests, and a 60-character bcrypt hash climbs past 400. That is glacial next to an in-band UNION attack that dumps a column in one shot. The trade-off is stealthiness on the response side and reliability: the attacker needs no error text and no visible data, only a consistent behavioral tell.
You might be thinking that so many requests would be obvious. On the response side they are quiet, but on the request side they are loud, and that is precisely where detection lives.
How Time-Based Blind SQL Injection Uses Delays as an Answer
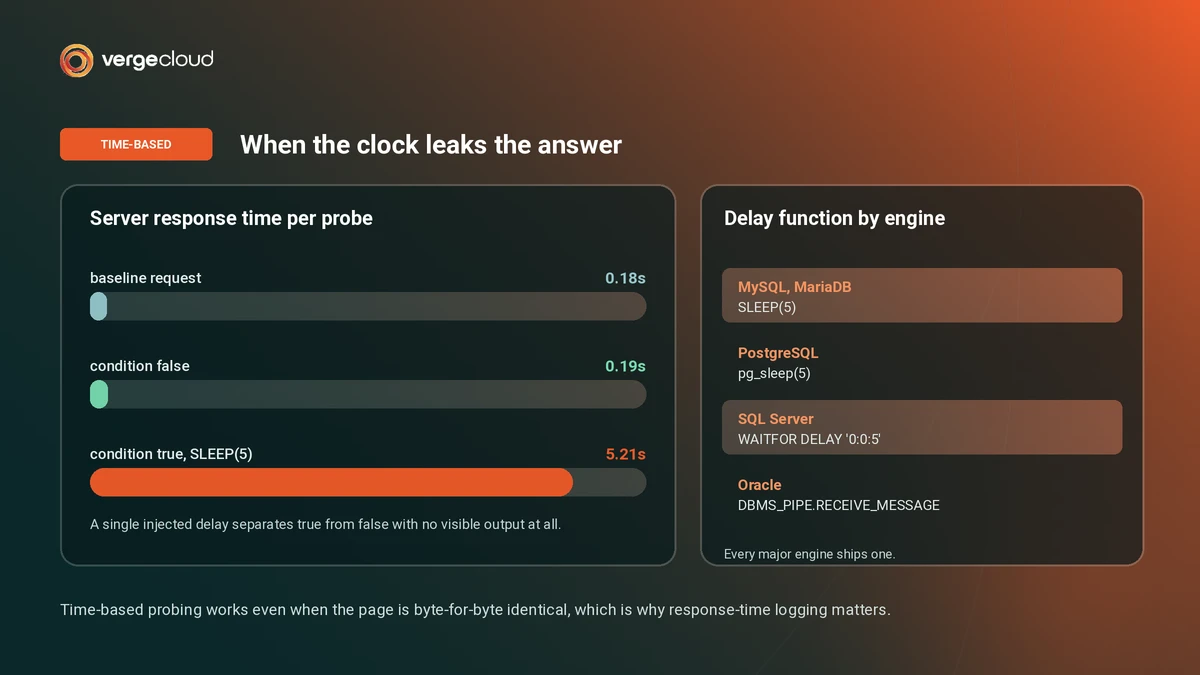
Time-based blind injection is used when the page looks byte-for-byte identical no matter what you inject. With no page difference to read, the attacker injects a conditional delay and measures the response time. A slow response means the condition was true, a fast one means false.
The delay comes from a database function. Every major engine ships one, so the payload is tailored to the backend:
If the injected condition holds, the database waits five seconds before answering and the whole HTTP response is delayed by that amount. The attacker reads the truth of the condition straight off the clock, then walks the data character by character exactly as in the boolean case.
“Time-based blind SQL injection is a subtype of blind SQL injection where the attacker observes the behavior of a database server and application in reaction to requests that combine legitimate queries with SQL commands that cause time delays.”
Time-based extraction is the noisiest technique on your infrastructure. A parameter that suddenly forces the same route to respond in 5-second multiples is a strong signal, which is why logging response duration per route matters more here than almost anywhere else.
Why time-based attacks are both slower and easier to catch
Injecting real delays makes the attack far slower than boolean probing, because every true condition costs seconds of wall-clock time. That same delay is a gift to defenders. Response-time outliers on one route, repeated hundreds of times, stand out sharply in logs and are hard to disguise as normal traffic.
Real Blind SQL Injection Vulnerabilities and Their Impact
Blind SQL injection is not a museum piece. It shows up in current, tracked vulnerabilities across widely used software, and it maps to CWE-89, which ranks second on the 2025 CWE Top 25 Most Dangerous Software Weaknesses.
Recent examples make the pattern concrete:
- CVE-2025-64492 is an authenticated time-based blind SQL injection in SuiteCRM versions 8.9.0 and below, allowing an attacker to infer data by measuring response times and enumerate database, table, and column names.
- CVE-2025-66313 is a time-based blind SQL injection in ChurchCRM, where an injected SLEEP() produces deterministic server-side delays that prove input reaches the query unparameterized.
- CVE-2025-24799 enables an unauthenticated attacker to run time-based blind SQL injection through an inventory endpoint and extract usernames, password hashes, and API tokens.
Across these cases, the payoff is the same: data exfiltration one inference at a time, often ending in credential theft, privilege escalation, or full database access. Attackers rarely stop at reading one field once they have a working oracle, and blind SQLi routinely lands near the top when teams audit their application security vulnerabilities.
The broader lesson is that suppressing errors and hiding output does not remove the flaw. It only forces the attacker to switch from reading data directly to inferring it, and tooling makes that switch cheap. This is a specific case of a broader injection attack class, where untrusted input is treated as executable code, and it sits alongside related database and parser flaws such as XXE attack vectors that exploit the same root cause of mixing data and instructions.
How to Detect Blind SQL Injection in Your Logs
Blind SQL injection is quiet in the response but loud in the request stream. Detection comes from correlating request volume, timing, and payload shape rather than watching for a single smoking gun.
Focus on four signals:
- Volume on one parameter. Hundreds of near-identical requests hitting a single input in a short window is the classic footprint of automated extraction.
- Inference keywords in input. SUBSTRING, ASCII, CASE WHEN, SLEEP, BENCHMARK, and WAITFOR rarely belong in legitimate user input.
- Response-time outliers. On time-based attacks, one route shows a p99 far above its median, often in clean 5-second steps.
- Body-length flapping. The same 200 status returns two distinct body sizes as the attacker toggles true and false conditions.
No single signal is conclusive on its own. Volume on one parameter combined with a timing outlier on the same route, or a probe pattern that walks a value character by character, is what turns noise into a confident detection. Feeding request duration and per-parameter request counts into your monitoring, backed by global edge security, lets you catch the extraction while it is still running rather than after the data is gone.
If you log only status codes and byte counts, time-based extraction can run for hours unnoticed. Add response duration per route to your access logs before you need it, not during an incident.
How to Prevent Blind SQL Injection at Every Layer
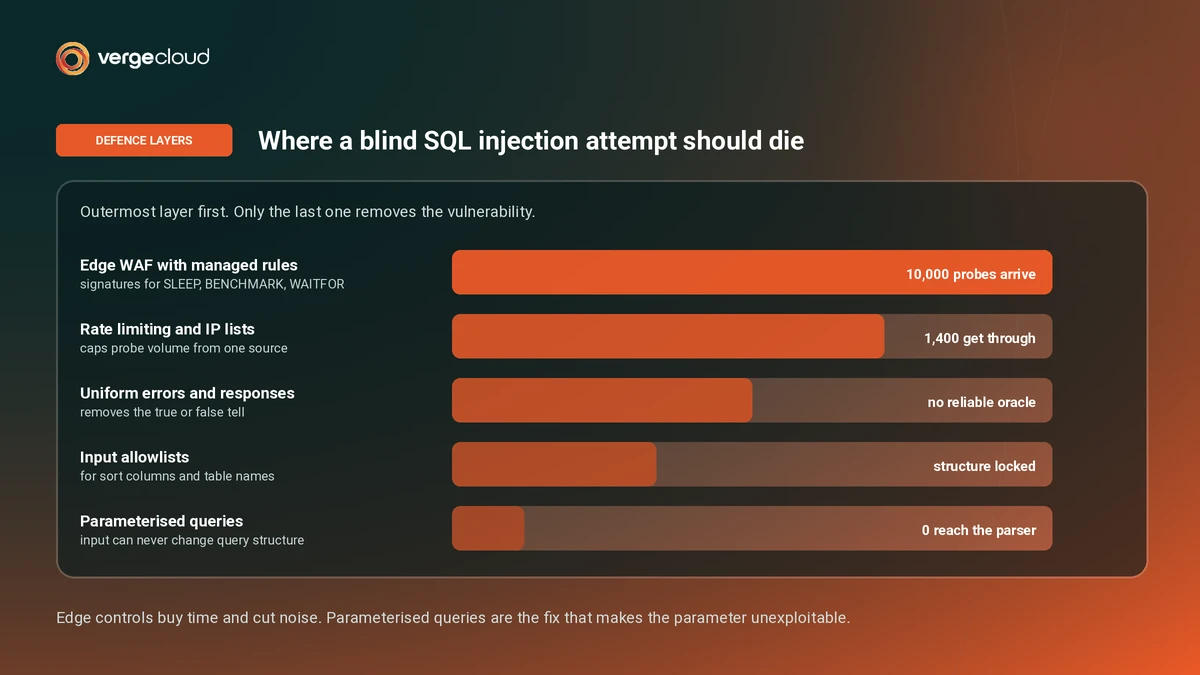
The vulnerability is fixed in the code, but a resilient defense stacks several layers so that most probes never reach the database and the ones that do cannot change the query. Only the innermost layer removes the flaw. The outer layers cut volume, remove the true-or-false tell, and buy your team time.
Parameterized queries remove the vulnerability
Parameterized queries, also called prepared statements, send the SQL structure and the user data to the database separately. Input can never change the query structure, so an injected SUBSTRING or SLEEP is treated as a literal value and does nothing. This is the fix. Every other control is defense in depth around it.
Allowlist the parts that cannot be parameterized
Some query elements, like a sort column or an ORDER BY direction, cannot be bound as parameters. Several real CVEs, including bypasses of earlier fixes, live exactly here. Validate these against a fixed allowlist of permitted values rather than escaping them, so the attacker has no path to inject a subquery in the sort position.
Use edge controls to cut probe volume and noise
Blind extraction needs many requests, which makes the edge a natural chokepoint. A managed ruleset on a firewall solution flags the SLEEP, BENCHMARK, and WAITFOR signatures these attacks depend on, while rate limiting caps how many probes one source can send before it is throttled, so an extraction that needs 10,000 requests never gets the budget to finish.
Once a probing source is identified, Custom IP Lists let you block the offending addresses at the edge, and routing traffic through a secure CDN keeps that inspection and throttling close to the user rather than at your origin. These controls do not replace parameterized queries; they reduce the noise reaching the parser and slow attackers enough for detection to fire.
Two more habits round out the defense. Return uniform errors and response bodies so there is no reliable true or false oracle for boolean probing, and run the application database account with least privilege so a successful read cannot escalate into writes or administrative commands.
Managed WAF rules and rate limits are conservative on purpose and will occasionally challenge legitimate automation. Tune them against your real traffic, but do not disable them to fix a false positive during an active probing campaign.
Blind SQL injection also overlaps with authorization mistakes. If an attacker can reach a parameter they should never touch, the impact widens, which is why fixing injection sits next to closing broken access control gaps, and why aligning your rules with the OWASP Core Rule Set gives you a tested baseline of signatures to build on.
Final Thought on Blind SQL Injection
Blind SQL injection proves that hiding output is not the same as being secure. The database still answers the attacker’s questions; it just answers through page behavior or response time instead of visible data. The single control that removes the flaw is the parameterized query, because it stops user input from ever altering query structure.
Treat everything else as defense in depth. Allowlist the query parts you cannot parameterize, log response duration and per-parameter request volume so you can see an extraction in progress, and use edge controls to cut probe volume and buy time. Get the code right first, then wrap it in layers that make an attacker’s job loud, slow, and easy to catch.
Common Questions About Blind SQL Injection
Is blind SQL injection more dangerous than classic SQL injection?
The impact is the same, since both can read or modify the entire database. Blind injection is slower to exploit but often harder to detect on the response side, so it can run longer before anyone notices. The severity depends on the data exposed, not on which technique retrieves it.
Can a web application firewall stop blind SQL injection on its own?
A WAF blocks many probes and slows extraction, but it is not a complete fix. Attackers use encoding tricks and tamper scripts to bypass signatures, so a WAF should sit in front of parameterized queries, not replace them. Use it to cut volume and trigger detection while the code-level fix removes the vulnerability.
How long does a blind SQL injection attack take?
It depends on how much data and which technique. Boolean-based probing reads a character in about seven requests, so a short password may take under a minute of automated requests, while time-based attacks are slower because each true condition costs real seconds. Extracting a large table can run for hours, which is why request-volume monitoring is effective.
Which tools do attackers use to automate blind SQL injection?
sqlmap is the most common, and it detects and exploits both boolean-based and time-based blind injection automatically. Because these tools fire hundreds to thousands of near-identical requests at one parameter, that traffic pattern is also one of the clearest fingerprints defenders can alert on.
