
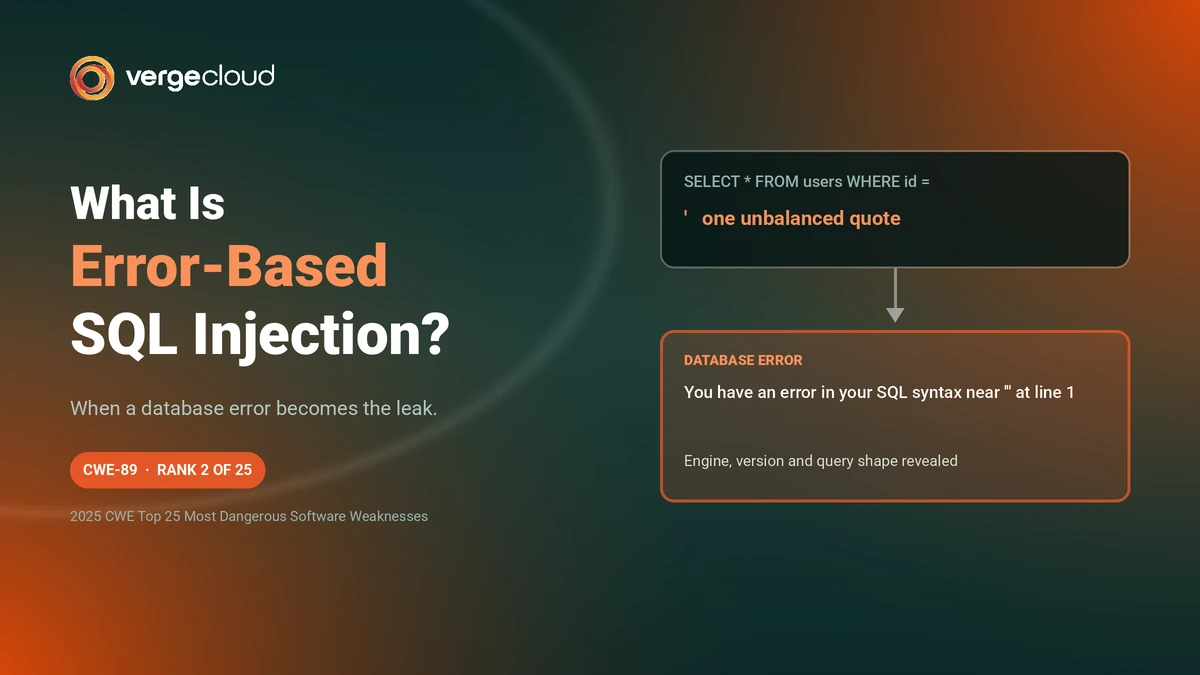
Error-based SQL injection is an attack that forces a database to fail on purpose so the resulting error message leaks data back to the attacker. When an application passes unfiltered input into a query and then prints the raw database error, that message can carry table names, column values, and even the database version straight to the browser. It sits under CWE-89, which ranked second on the 2025 CWE Top 25 Most Dangerous Software Weaknesses. This guide breaks down how the technique works, how it differs from other variants, how to spot it in your own traffic, and the layered controls that shut it down. The first clue is often a message you did not expect to see.
Key Takeaways
- Error-based SQL injection extracts data through database error messages rather than through normal page output.
- It depends on two conditions at once: an injectable query and verbose errors that reach the user.
- The wording of an error reveals which database engine is in use, which guides the rest of the attack.
- It is faster and quieter than blind techniques because one malformed request can return an actual value.
- SQL injection is CWE-89, which sits at number two on the 2025 CWE Top 25.
- Parameterized queries remove the root cause; suppressing verbose errors removes the leak channel.
- A layered setup pairs edge filtering with least-privilege database accounts so one gap does not become a breach.
How Error-Based SQL Injection Works
Error-based SQL injection works by breaking a query so the database throws an error, then reading the data that error carries. The attacker supplies input that the application concatenates directly into a SQL statement, which is the same root flaw behind every injection attack. Instead of asking for a page of results, the payload asks the engine to perform an illegal operation whose failure message includes the value the attacker wants.
The sequence is short. A parameter such as a product id receives a single quote, the statement no longer parses, and the engine responds with a syntax error. That first error confirms the input reaches the query unescaped. From there, functions that force a type conversion or an XPath failure can be used to place a subquery result inside the error text itself.
The payoff is directness. The attacker does not have to reconstruct hidden logic or guess one character at a time, because the answer is printed in the response. That is why this variant is often the first one a tester reaches for when an application still shows raw database output.
The single quote below turns a valid lookup into a parse failure, and the conversion trick pushes a subquery into the error text.
-- normal request
GET /product?id=7

-- probe: one quote breaks the statement
GET /product?id=7'

-- MySQL: force the version into the error message
GET /product?id=7 AND extractvalue(1, concat(0x7e, version()))
Why Database Error Messages Are the Real Problem
The vulnerability is the injectable query, but the leak is the verbose error. MITRE tracks that exposure separately as CWE-209, the generation of an error message containing sensitive information. A perfectly injectable query returns far less to an attacker when the database error never reaches the browser.
A raw error does three jobs for an attacker at once. It confirms the input is unescaped. Its wording, unique to each product, names the engine. And it becomes the channel that carries extracted values back out. Every disclosed detail shortens the path to a working exploit.
You might be thinking a firewall already covers this. A network firewall inspects ports and addresses, not the meaning of a SQL string inside an allowed HTTPS request, which is the distinction explored in this comparison of WAF vs firewall. The error text slips through because the request itself looks legitimate.
“The sensitive information may be valuable information on its own, or it may be useful for launching other, more serious attacks.”
How Attackers Read the Database From an Error
Attackers read a database from its errors by fingerprinting the engine first, then choosing functions that leak data through failure. The OWASP Web Security Testing Guide describes error-based extraction as forcing an operation whose result appears inside the error message. Different engines expose themselves through distinct wording, so the first failed query usually names the target.
Once the engine is known, the attacker picks a matching technique. MySQL families respond to XPath functions such as extractvalue and updatexml. SQL Server leaks through failed conversions where a string value cannot cast to an integer. Oracle and PostgreSQL each have their own equivalents. In every case the goal is the same: wrap a subquery so its output lands in the error string.
The table below maps common signatures to the engines that produce them, using the wording documented in the OWASP testing guide.
| Database engine | Characteristic error text | Common error-based technique |
|---|---|---|
| MySQL / MariaDB | You have an error in your SQL syntax | XML-related error functions such as EXTRACTVALUE() and UPDATEXML() |
| Microsoft SQL Server | Unclosed quotation mark after the character string | Conversion and type-conversion errors, such as CAST() and CONVERT() |
| PostgreSQL | unterminated quoted string at or near | Type-conversion and arithmetic errors, including CAST() and division-by-zero errors |
| Oracle Database | ORA-00933: SQL command not properly ended | Oracle-specific conversion and expression errors that expose database information |
The same signatures that help an attacker help a defender. Feeding these patterns into managed detection, such as the OWASP Core Rule Set, lets you flag probing attempts before extraction begins.
Error-Based Versus Blind SQL Injection
The difference is the output channel. Error-based injection returns data inside visible error messages, while blind SQL injection infers data from true or false behavior when no error is shown. Both exploit the same underlying flaw; only the way the answer comes back changes.
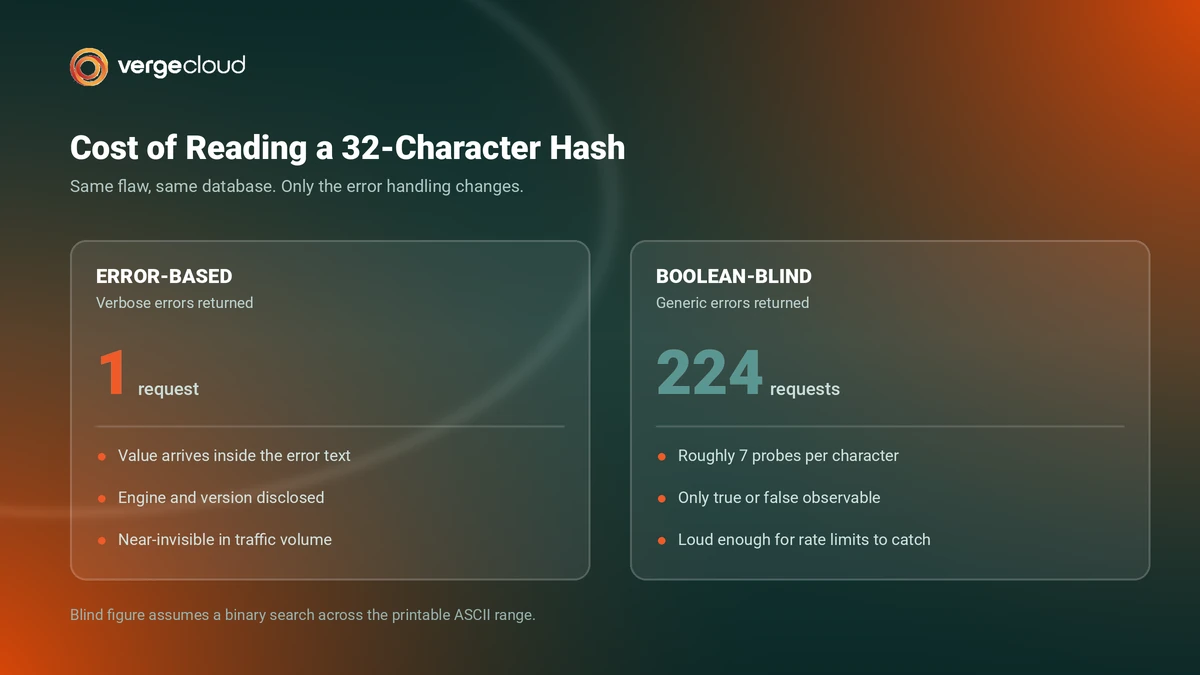
That difference decides speed. When errors are verbose, a single crafted request can return an actual value. When they are suppressed, the attacker falls back to boolean or time-based questions and reads the answer one bit at a time, which multiplies the number of requests by a large factor.
Yes, suppressing errors helps, but it does not fix the vulnerability. It forces the attacker onto a slower path rather than closing the door. The flaw still lives in the query, and a patient attacker will still reach the data.
How to Detect Error-Based SQL Injection
You detect error-based SQL injection by watching for the errors themselves and for the traffic patterns that precede them. The clearest signal is a database syntax or conversion error surfacing in an HTTP response, since a healthy application rarely leaks driver text to users.
Practical detection combines a few sources. Application logs that record database exceptions tied to specific parameters point straight at the weak input. Web server logs full of single quotes, comment markers, and function names such as extractvalue or convert reveal probing. Automated tools like sqlmap generate bursts of near-identical requests, which stand out against normal usage.
Because automated enumeration is noisy by design, request-volume controls double as an early warning. Sensible rate limiting slows a scanner enough to surface it in monitoring before it finishes mapping the schema.
What to review, in order:
- Search HTTP responses for database error strings reaching end users.
- Correlate application exceptions with the exact parameter that triggered them.
- Flag requests carrying quotes, comments, or known leak functions.
- Watch for repeated near-identical requests that signal automated tooling.
How to Prevent Error-Based SQL Injection
Prevention works on two fronts at once: remove the injectable query and remove the error leak. Parameterized queries, also called prepared statements, keep user input strictly as data so it can never change the structure of a statement. This single control eliminates the root cause across error-based, blind, and union variants alike.
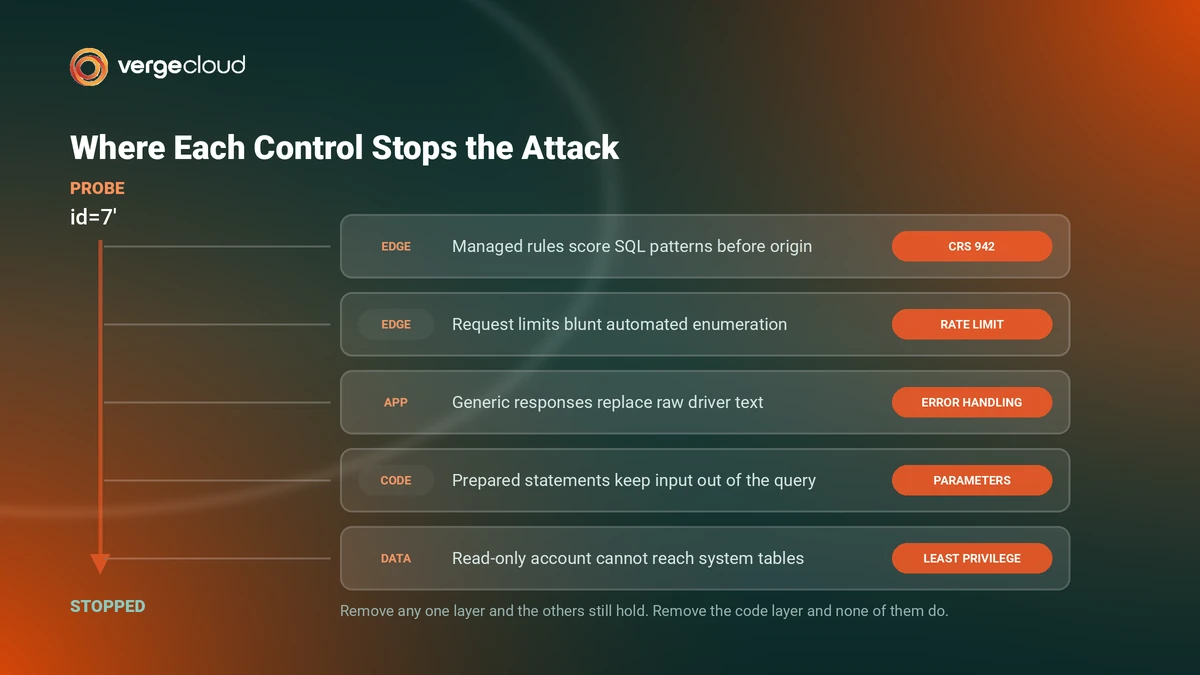
Suppressing verbose errors closes the disclosure channel. Return a generic message to users and send the full detail to a private log, which lines up with the CWE-209 guidance on not exposing sensitive information. Well-designed custom error pages give users a clean response while starving an attacker of clues.
Depth matters because layers cover each other. A reverse proxy WAF inspects requests before they reach the origin and scores SQL patterns for you. A least-privilege database account limits what any successful query can touch, so a foothold does not become full access, the way weak permissions turn into broken access control. For teams tuning detection against noisy applications, custom WAF rules cut false positives without lowering coverage.
What Error-Based Injection Looks Like in the Wild
SQL injection is not a theoretical risk, and the impact scales with the data behind the query. The clearest recent example is CVE-2023-34362 in Progress MOVEit Transfer, a critical SQL injection flaw that CISA added to its Known Exploited Vulnerabilities catalog in June 2023. Attackers used it to reach the underlying database of a widely deployed file-transfer product.
According to the NVD entry, an unauthenticated attacker could infer information about the structure and contents of the database and execute statements that altered or deleted elements, across MySQL, Microsoft SQL Server, and Azure SQL backends. The Cl0p group weaponized it at scale, and the incident became one of the largest data-theft campaigns tied to a single injection flaw.
One product is not the lesson here. A single injectable parameter, paired with a database that talks too much when it fails, can expose an entire records store. The controls in the previous section are what keep a probe from becoming that headline.
Final Thought on Error-Based SQL Injection
Error-based SQL injection stays dangerous for one reason: it turns a routine failure into an information source. The vulnerability lives in a query that trusts user input, and the damage lives in an error message that says too much. Close either and the attack weakens; close both and it stops.
Treat prepared statements as the fix and everything else as reinforcement. Suppress verbose errors, filter requests at the edge, and give your database accounts only the access they need. Layered together, these controls protect the data without punishing the users who depend on it.
Common Questions About Error-Based SQL Injection
Is error-based SQL injection still a real threat?
Yes. SQL injection is CWE-89, ranked second on the 2025 CWE Top 25 Most Dangerous Software Weaknesses, and error-based is one of its most direct variants. Any application that concatenates user input into a query and shows raw database errors is exposed.
Does hiding error messages fully prevent SQL injection?
No. Hiding errors removes the fastest extraction channel and pushes an attacker toward slower blind techniques, but the injectable query remains. Parameterized queries are what actually remove the vulnerability.
Can a web application firewall stop error-based SQL injection?
A WAF blocks many known injection patterns before they reach the application and is a valuable layer, but it is not complete on its own. It works best paired with parameterized queries and suppressed errors rather than as a single line of defense.
