
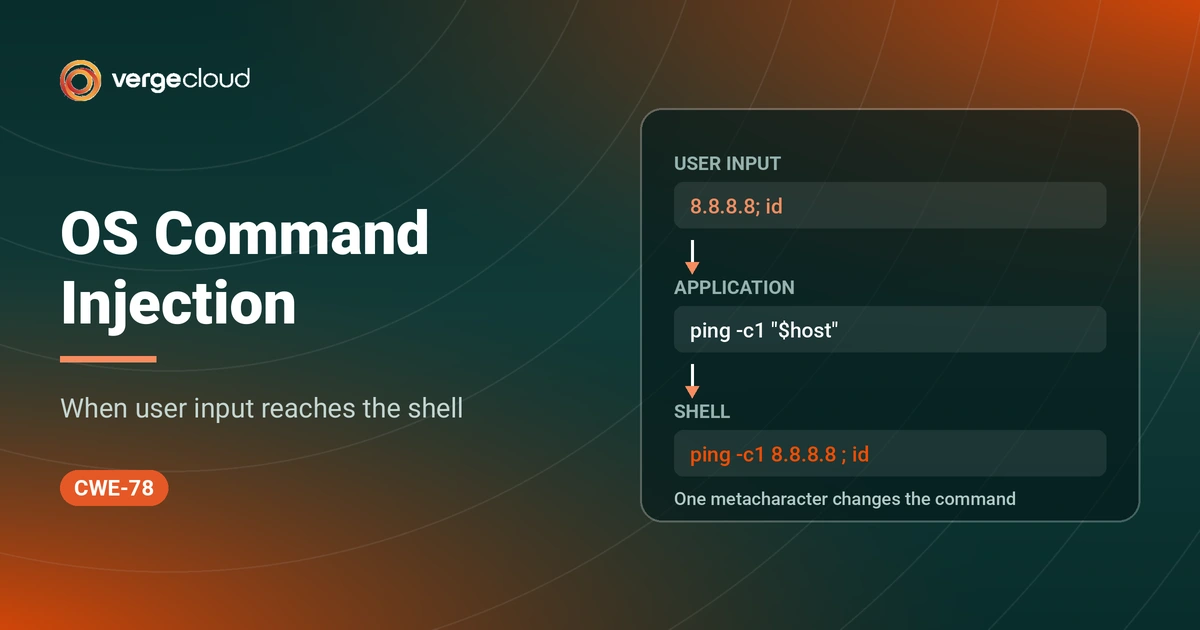
OS command injection is a flaw that lets an attacker run their own operating system commands on a server, because the application builds a shell command out of untrusted input. One character, a semicolon or a backtick, turns a single intended command into two, and the second one runs with whatever privileges the application holds. MITRE ranked CWE-78 first on the 2025 CWE Top 10 KEV Weaknesses list, ahead of every memory corruption class. This guide covers how input reaches the shell, where the flaw hides in real systems, how to detect it, and which controls hold. One of those controls does far less than most teams assume.
Key Takeaways
- OS command injection happens when an application passes untrusted input into a system shell, so an attacker can append commands that run with the application’s privileges.
- MITRE placed CWE-78 first on the 2025 CWE Top 10 KEV Weaknesses list, with 20 entries in CISA’s Known Exploited Vulnerabilities catalogue.
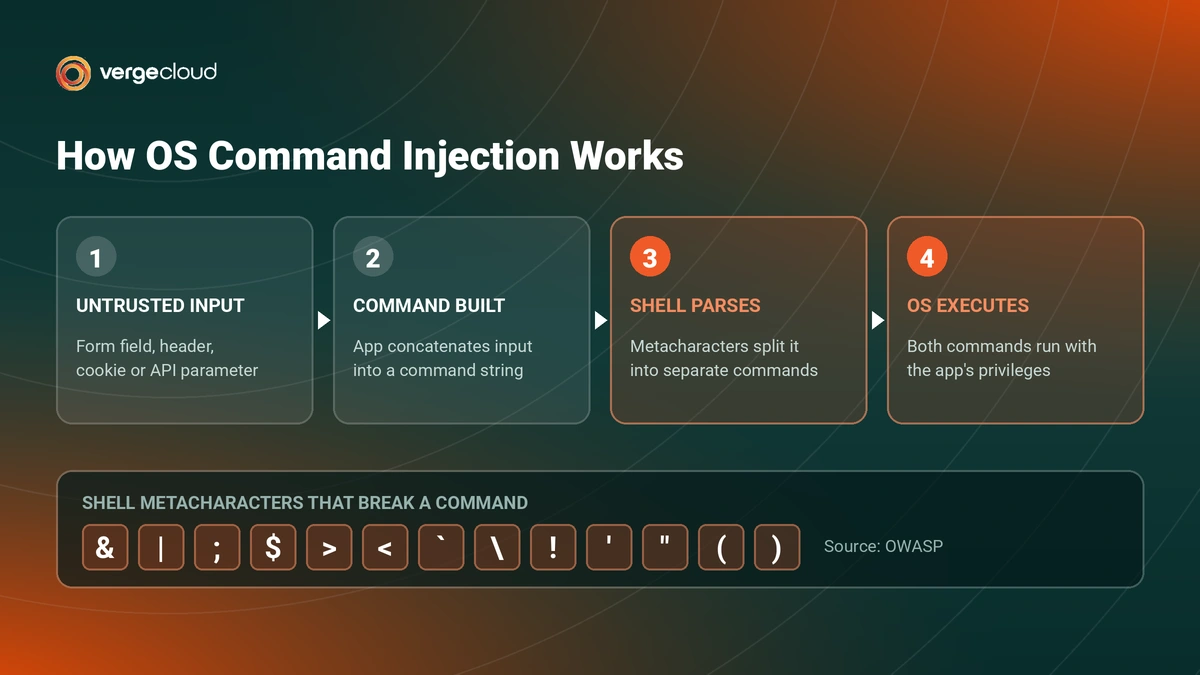
- Shell metacharacters such as the semicolon, pipe, ampersand, backtick and dollar sign are what split one command line into several.
- CVE-2024-3400 in Palo Alto Networks PAN-OS scored CVSS 10.0 and gave unauthenticated attackers root on internet-facing firewalls.
- The durable fix is architectural: call a language library instead of a shell, and pass each argument separately.
- Least privilege and outbound traffic restrictions decide how much damage a successful injection can do.
How Untrusted Input Reaches the Operating System Shell
The flaw appears the moment an application glues user-controlled data into a command string and hands it to a shell. The shell cannot tell which characters came from the developer and which came from the request. It parses the whole line and runs everything it finds. That one design choice separates an ordinary injection attack from full control of the host.
Think of the shell as a receptionist reading a note aloud. The note says call this number. Add a full stop and a second sentence, and the receptionist reads that out too, because nothing marks where the instruction was meant to stop.
The pattern fits in a few lines, which is why it survives code review.
// Vulnerable: user input
// concatenated into a shell string

exec("ping -c 1 " + req.query.host);

// Request: ?host=8.8.8.8;id

// Shell runs:
// ping -c 1 8.8.8.8 ; id

// Safe: no shell involved,
// arguments passed separately

execFile("ping", ["-c", "1", req.query.host]);
“Command injection attacks are possible largely due to insufficient input validation.”
How it Differs from Code Injection and Database Injection
Code injection adds attacker-written code to the application runtime. Database injection, whether classic SQL or NoSQL injection, manipulates a query a database engine parses. OS command injection needs neither. The attacker writes no code and touches no database. They extend a command the application was already going to run, using syntax every Unix shell has understood since the beginning. That is why the payload is often two characters and the impact is often total.
If the mechanism is that simple, why does it keep appearing in shipped products?
Where Command Injection Hides in Production Systems
It clusters in code that wraps a command-line tool. Wherever shelling out looked faster than finding a library, there is a candidate, and that decision is most common in the parts of a stack nobody rewrites.
- Diagnostic endpoints calling ping, traceroute or nslookup from a router or admin panel
- File conversion and media processing that shells out to ImageMagick, ffmpeg or Ghostscript
- Backup, archive and log rotation scripts that build paths from user-supplied names
- Security appliance, VPN and load balancer management interfaces
- CI/CD steps that interpolate a branch name or pull request title into a shell command
- Embedded and IoT web interfaces where the web layer already runs as root
Two cases show the range. CVE-2016-3714, ImageTragick, let a crafted image carry shell metacharacters into ImageMagick’s delegate handling, exposing any site that accepted avatar uploads. CVE-2014-6271, Shellshock, turned Bash environment variables into an execution primitive and made CGI scripts attack surface overnight. Neither involved a login form. Both started with a file or header the application trusted, the same root cause behind local file inclusion.
Why CWE-78 Sits at the Top of the Exploited Weakness List
Because attackers use it more than anything else. In the 2025 CWE Top 10 KEV Weaknesses list, MITRE ranked OS command injection first with a danger score of 80.43 and 20 CVEs in CISA’s Known Exploited Vulnerabilities catalogue. Second place scored 51.89. That gap is a tier, not a margin.
| Weakness | CWE | CVEs in KEV | Danger score |
|---|---|---|---|
| OS Command Injection | CWE-78 | 20 | 80.43 |
| Use After Free | CWE-416 | 14 | 51.89 |
| Out-of-bounds Write | CWE-787 | 12 | 50.39 |
| Missing Authentication for Critical Function | CWE-306 | 11 | 50.27 |
| Deserialization of Untrusted Data | CWE-502 | 11 | 46.31 |
Two entries explain the ranking. CVE-2024-3400 in the GlobalProtect feature of Palo Alto Networks PAN-OS scored CVSS 10.0 and let an unauthenticated attacker execute code with root privileges on the firewall itself, CVE-2024-21887 in Ivanti Connect Secure scored CVSS 9.1 and was chained with an authentication bypass until CISA issued an emergency directive ordering federal agencies to act.
You might be thinking this is a legacy problem confined to old PHP code. Here is what most teams miss: the highest-impact cases were not in anyone’s web application. They were in the security appliances sitting in front of it, bought to reduce risk, deployed at the edge and running as root. A flaw there exposes everything behind it.
So how do you find the flaw in your own systems first?
How to Detect OS Command Injection Before an Attacker Does
Detection splits in two, depending on whether command output comes back in the response. In-band injection returns the result, so one request confirms the flaw. Blind injection returns nothing useful, so confirmation comes from side effects.
Blind testing works by inference, the way you knock along a wall to find a stud. You never see inside, you read the response. The logic mirrors blind SQL injection: make the server behave differently in a way you can measure, then narrow down.
- Map every parameter that could reach a system utility, including headers, cookies, filenames and JSON fields, not just visible form inputs.
- Test in-band first by appending a separator and a harmless command with distinctive output, such as an echo of a fixed string.
- Move to time-based probes when nothing comes back. A delay that reliably adds ten seconds to the response is strong evidence.
- Use out-of-band callbacks for the hardest cases: trigger a DNS or HTTP request to a host you control and watch for the lookup.
- Confirm on a staging copy, then check what the process can reach: file system, credentials, internal services and outbound network.
Five Layers That Prevent OS Command Injection
These layers are ordered by how much risk they remove, not by ease of deployment. The first two eliminate the vulnerability. The last three limit what an attacker gets when the first two were missed.

- Avoid the shell entirely. Most shell calls do something a language library already does. Creating a directory, resolving a hostname or resizing an image rarely needs an interpreter.
- Parameterize the call. When you must run an external binary, pass the command and each argument as separate values so the operating system never sees one concatenated string.
- Validate against an allowlist. Define the permitted commands and a strict argument pattern. A regular expression allowing only lowercase letters and digits beats a denylist, which always misses an encoding.
- Run with least privilege. Give the process a single-purpose account, no root, no shared service user, no filesystem access beyond what it needs. That turns a total compromise into a contained one.
- Filter and watch at the edge. Signature matching, egress restrictions and alerting on unexpected outbound connections give you detection and a virtual patch while a vendor fix is tested.
The fifth layer is where edge security earns its place. It does not repair the code and is never the fix.
Can a WAF Prevent OS Command Injection?
Partly, and the distinction matters. A web application firewall inspects requests before they reach the origin and blocks payloads matching a known pattern. Against opportunistic scanning and published exploit code it works immediately. Against a payload shaped for your specific application, it is a delay rather than a barrier.

| Attack pattern | Edge filtering result | Why |
|---|---|---|
| Raw metacharacters in a query string or header | Blocked | Signatures match separators such as a semicolon, pipe or backtick before the request reaches the origin |
| Known exploit signature, for example CVE-2024-3400 | Blocked | Vendor and community rules ship a specific pattern for the payload |
| Blind payload with no visible output | Often missed | Nothing in the response distinguishes it from a normal request |
| Double encoded or nested payload | Often missed | The application decodes the value after inspection has finished |
| Injection through an authenticated appliance CLI | Not seen | The request never crosses the edge filtering path |
The practical answer is to treat filtering as coverage, not as a cure. Well-tuned WAF rules stop the noise, catch published exploit signatures the day they land, and give engineering room to schedule a real fix. That is a measurable benefit. It is not the same as closing the hole, and any team that treats it that way will eventually meet a blind payload with no response to match against.
Final Thought on OS Command Injection
OS command injection stays at the top of the exploited weakness rankings for one reason: the fix is architectural, and architecture is what teams postpone. Other injection classes were squeezed by better defaults such as prepared statements and template escaping. Shell calls never got that treatment, so the same concatenation pattern still ships in new firmware today.
The guidance is short. Find every place your code hands a string to an interpreter and remove the interpreter where you can. Where you cannot, pass arguments separately and validate against an allowlist. Then assume one instance was missed, and give that process almost no privileges and almost no outbound reach. Edge filtering sits on top of that work, not in place of it.
Common Questions About OS Command Injection
Is OS command injection the same thing as remote code execution?
Not quite. Remote code execution describes the outcome, running attacker-chosen code on a target. OS command injection is one route to it, and a direct one, because injected commands run as soon as the shell parses them. Deserialization flaws and memory corruption reach the same place by other paths.
Does escaping shell metacharacters make the call safe?
It reduces risk without removing it. Escaping rules differ between Bash and Windows interpreters, encoding layers can reintroduce a character after your filter runs, and argument injection still works when an escaped value becomes a flag rather than a value. Treat escaping as a fallback for code you cannot restructure.
Can command injection happen in a containerised or serverless application?
Yes. A container changes what an attacker can reach, not whether the injection succeeds. A function that shells out to a converter is as vulnerable inside one as outside. The difference is blast radius, which is why a minimal image, a non-root user and restricted egress matter.
